REST API Documentation Standards and Formats
OpenAPI 3.1 provides the standard format for REST API specifications across layers of documentation.
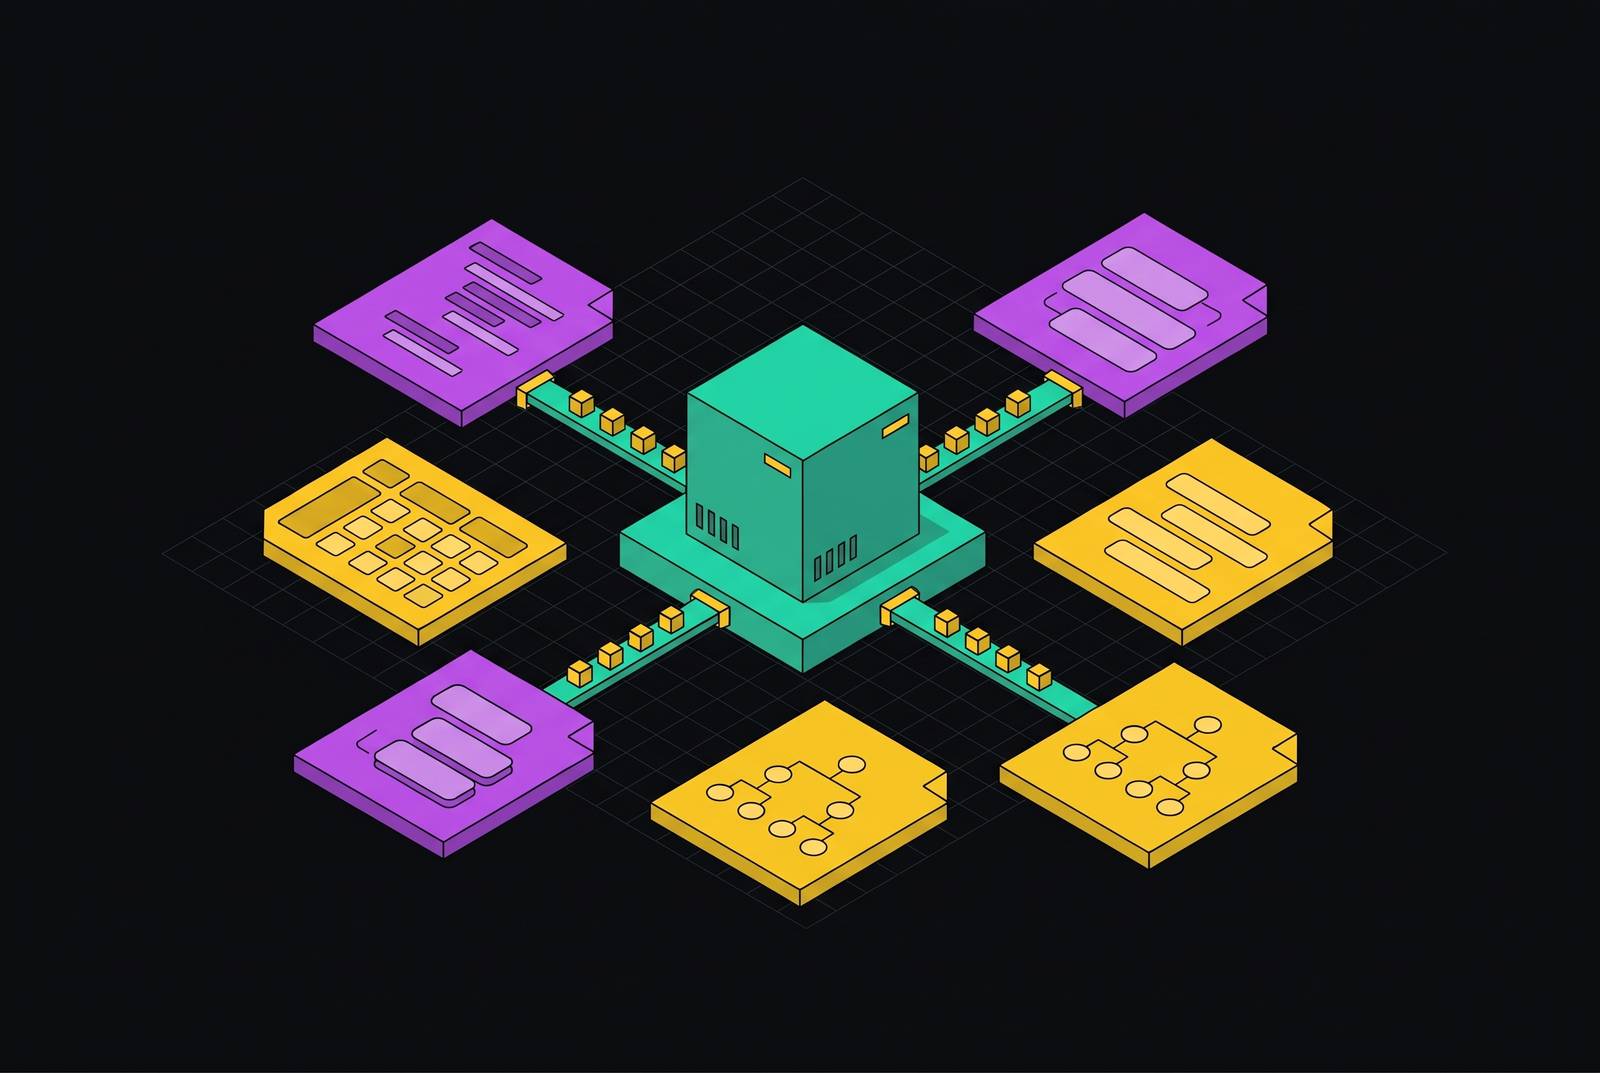
REST API documentation standards and formats provide a blueprint for usable documentation, with OpenAPI 3.1 at its center. The specification sets out the machine-readable contract, but it cannot take the place of reference material, onboarding guidance, or change history. Reliable documentation comes from giving each layer a clear role and maintaining them as connected parts of the same API.
What REST API documentation is actually made of
The machine-readable specification describes the API for tools and generators. Reference documentation explains endpoints, parameters, responses, and error codes to developers as they work through an integration. Conceptual guides, quickstarts, and tutorials serve developers in their first session, while changelogs and versioning artifacts help existing integrators track changes. These layers answer different questions about the same interface.
Their boundaries explain why a complete specification can still leave an API poorly documented. A developer may find every parameter definition but still have no clear way to get through authentication and make a working request. First-session failures can lead to abandonment rather than support tickets, with time-to-first-call exposing the friction.
Why OpenAPI became the dominant format for REST specifications
OpenAPI defines endpoints, schemas, authentication methods, and responses in JSON or YAML that humans and automated tools can interpret. Its dominance comes from the surrounding toolchain. Code generators build SDKs from the definition, gateway plugins use it to enforce policies, and developer portals show it as interactive reference material. Once those systems share a format, replacing it affects more than the documentation renderer.
That fit is specific to synchronous HTTP request-response APIs. AsyncAPI uses JSON or YAML for event-driven APIs involving message brokers, WebSockets, and streaming protocols. OpenRPC describes JSON-RPC APIs in JSON, while Protocol Buffers uses.proto files for gRPC services and high-performance binary communication. Each format serves its own architectural context. Zalando’s RESTful API and Event Guidelines require OpenAPI specifications, treating the format as a first-class engineering artifact.
What OpenAPI 3.1 changes and why teams starting new projects should target it
OpenAPI 3.1 is the appropriate target for new projects because it fully aligns with JSON Schema draft 2020-12. This fixes the compatibility gap in 3.0 so that external schema libraries can work without translation layers. Tools targeting 3.1 can therefore validate schemas more precisely.
Moving an existing specification to the new version means changing its schema syntax as well as its version label. Starting with 3.1 avoids planning that conversion into a new project. Zalando’s guidelines encourage 3.1, especially for new specifications, and most current generators, validators, and documentation platforms have aligned with it. The recommendation rests on the standard’s schema compatibility.
The structural content that every REST API reference section must cover
The reference must give the HTTP method and URL path for each endpoint and define its parameters. Request documentation must give the data types, say which fields are required and optional, and set out the valid value ranges. Response documentation must provide status codes, schemas, and example payloads for success and failure. Error codes need causes and troubleshooting guidance.
The reference must also explain request quotas, time windows, and headers showing remaining capacity. Authentication documentation needs the scheme, credential location, and scopes required by each endpoint. Where SDKs are available, instructions for each language must show how to install them, with examples of common operations that use actual request syntax. These details connect the declared contract to executable use.
A reference that developers can search needs navigation that works the same way throughout, deep-linkable URLs, and a list of every endpoint, along with a getting-started path that leads to a working call without leaving the page. Side-by-side samples and browser consoles let developers read how a request works and then test it with their own credentials. Clear versioning and deprecation policies complete the contract by identifying what is stable and when deprecated behavior will end.
URL structure, HTTP method, and naming conventions that the reference layer enforces
The HTTP method supplies the verb, while the URL identifies the resource. That makes /orders preferable to /getOrders, which duplicates the method’s role. Collections have plural resource names, and /orders/42 points to one item. Zalando’s guidelines make pluralized resource names mandatory. They also specify kebab-case for path segments, snake_case for query parameters, and UPPER_SNAKE_CASE for enum values.
Nesting should stop at two levels, and deeper relationships should use top-level resources and filters. For example, /items?orderId=3 avoids the depth of /companies/1/users/2/orders/3/items/4. Method semantics need equal consistency. GET retrieves, the replacement method replaces, and the removal method removes, with each being idempotent, while POST creates and is not idempotent, and PATCH performs a partial update that is sometimes idempotent.
Error structure provides another predictable reference anchor. Every error response should have a machine-readable code and a human-readable message, and validation failures should also name the field involved. Clients parse the code. Stable conventions make the reference scannable without requiring developers to relearn the contract for every endpoint.
Data format standards that specifications must declare explicitly
Naming conventions do not resolve ambiguity inside a payload. Dates, numbers, and null values need explicit declarations because inconsistent interpretations can produce subtly wrong behavior without clear failures. Zalando’s guidelines require JSON payloads and snake_case property names, with UPPER_SNAKE_CASE enum values. They also define string-typed date and time formats, including date, time-local, date-time-local, time, date-time, duration, and period, based on RFC 3339, a subset of ISO 8601.
Numeric declarations need the same precision as timestamps. The formats for number and integer types must be stated clearly to avoid precision errors when languages handle floating-point values in different ways. Null and absent properties also need consistent semantics because clients may depend on their distinction. Treating them as interchangeable creates breaking-change risk. These declarations belong in the specification, where validators and generators can enforce them.
Versioning and deprecation policy as documentation requirements, not engineering afterthoughts
Versioning strategy and deprecation policy need to exist from the start. Retrofitting them onto a live API can disrupt the integrations they are intended to protect. URI versioning, such as /v1/orders, is common and easy to debug because the version appears in every request log. Header-based versioning keeps URLs clean but reduces discoverability. Zalando’s guidelines require media type versioning and ban URL versioning, so the choice still comes with trade-offs and has no convention that applies everywhere.
Deprecation timelines must be stated before removal becomes imminent. The standards-body-defined Sunset header in RFC 8594 and Deprecation header in RFC 9745 communicate lifecycle changes programmatically. Zalando’s guidelines also require deprecation in the specification itself. Because their guidelines require semantic versioning, the specification’s version is another way to show what has changed, with major versions marking breaking changes, minor versions marking additive changes, and patches marking fixes.
How the spec-as-source-of-truth model keeps reference documentation from drifting
Documentation drift emerges when the specification, implementation, and published reference describe different behavior. Separate maintenance creates the conditions for that divergence. Generating reference documentation directly from the API definition and deploying it through CI/CD removes the drift caused by editing reference pages independently. The specification becomes the canonical input for SDKs, code examples, and interactive documentation.
An OpenAPI change provides a precise review trigger because the changed operation or schema identifies the affected interface. Teams can mark the directories and configuration files defining the public API so that relevant pull requests require a documentation check. Automation handles structural, repetitive work such as parameter tables and code samples, while technical writers remain responsible for tutorials, conceptual explanations, and onboarding narratives. This division preserves judgment and limits the downstream cost of stale documentation, which AI agents can propagate into generated integration code.
How AI agents read API documentation and what that changes about writing it
AI agents that read documentation through the Model Context Protocol use endpoint descriptions to choose tools. An MCP server exposes endpoints as tools, and an MCP client consumes them. The OpenAPI description field becomes a primary selection signal. Vague text can therefore confuse readers and cause the wrong operation to be chosen.
The distinction is visible in the descriptions themselves. “Returns user data” gives little basis for selecting an operation, while “Retrieves a paginated list of orders for a given customer, filtered by status and date range” identifies the resource, scope, and filters. Descriptions derived mechanically from method names often lack that specificity. For AI-mediated discovery, each description must distinguish its endpoint unambiguously. Machine-readable specifications also need to be open to the public because AI coding tools that run in editors cannot use documentation they cannot read.
What the eight best-documented public APIs demonstrate about putting the standards into practice
Stripe unifies reference material and tutorials in a three-column layout containing navigation, prose, and code samples. Its examples cover Python, Node, Ruby, PHP, Java, Go, and.NET, and many endpoints include a “Try It” console. Its per-endpoint examples use curl, with separate JavaScript and Ruby SDK guides, granular permission tables, and published OpenAPI specifications for product tiers and supported date-based versions.
Twilio connects explanation to execution through sample applications for SMS, voice, and video that are deployable in minutes. Its searchable, OpenAPI-driven reference includes full SDK invocations. Slack makes authentication distinctions explicit at each endpoint. Its documentation identifies required token types and exact scopes across OAuth scopes, bot tokens, and user tokens, with webhook documentation providing another established pattern.
AWS emphasizes depth through service references, tutorials, architectural patterns, IAM policy examples, and CLI and SDK samples, supported by unified search. That breadth comes with less navigational polish. Google Maps uses progressive disclosure to lead developers from quickstarts to advanced use cases in the same documentation. Its embedded examples can be copied and modified on the page.
Shopify separates the Storefront API and Admin API clearly in navigation while emphasizing authentication, webhook patterns, and operation-specific access scopes. Postman makes documentation executable through rendered request-response views and collections developers can fork into their workspace through the Run in Postman button. The examples differ in their presentation choices. Their shared strength is the connection between reference content, explanations, and working requests, rather than any single layout or sample-language count.
How authentication, rate limiting, and caching requirements belong in the spec, not just the prose
Operational requirements need machine-readable declarations so gateways, validators, and generated SDKs can enforce them. Zalando’s guidelines require secured endpoints with defined and assigned permission scopes. Authentication choice follows the audience, including API keys for server-to-server flows, OAuth 2.0/OIDC for user-acting flows, and mTLS for high-security partner integrations. Credentials must go in Authorization headers and must never go in URL query strings. Query strings expose them to server logs, Referer headers, browser history, and CDN logs.
Rate limits also need to be set out in a machine-readable contract. Every public endpoint needs a limit, with 429 Too Many Requests and Retry-After returned when it is reached. X-RateLimit-Remaining and X-RateLimit-Reset headers allow clients to self-throttle before that point. Zalando’s guidelines require 429 responses with rate-limit headers. Quotas described only in prose cannot provide that feedback.
Caching behavior belongs in the same specification. Cache-Control and ETag headers let HTTP caches reuse responses, and Zalando’s guidelines require cacheable GET, HEAD, and POST endpoints to be documented as such. Mutation endpoints must have a Cache-Control directive that is set to no-store. Conditional requests using If-None-Match with ETags return 304 Not Modified when the resource is unchanged, reducing bandwidth without changing the API contract.
Why the changelog is a required documentation layer, not an optional release artifact
A reference describes the current API, but existing integrators also need its change history. A practical changelog architecture serves them at different levels. A repository’s CHANGELOG.md follows Keep a Changelog categories, including Added, Changed, Deprecated, Removed, Fixed, and Security. A public changelog explains user impact with less implementation detail, while a newsletter or digest reaches integrators who do not watch the repository.
These artifacts must remain connected to the specification. Deprecation recorded only in a release announcement leaves the machine-readable contract incomplete, while consistent semantic versioning makes breaking changes, additions, and fixes recognizable through version numbers. Clear history also gives developers evidence against which to judge claims about stability. Its absence is not a neutral signal. The changelog and specification document the same API across time and in its current state, and both require the same maintenance discipline.